
BrowserLeaks Login: What It Detects and Safer Alternatives
BrowserLeaks Login: What It Detects and Safer Alternatives
If you searched for "BrowserLeaks login," you probably landed on a page that claims to show which social networks you are signed into — without you typing a single password. That page is real, and the technique behind it is older than most people assume. This article explains what BrowserLeaks login detection actually does, why it still works in some browsers, and how to check whether your own setup is exposed.
What the BrowserLeaks login test actually does
BrowserLeaks Login: What It Detects and Safer Alternatives - What the BrowserLeaks login test actually does.
The tool at browserleaks.com/social is a demonstration of cross-origin login detection. It does not ask for credentials and it does not read your cookies directly. Instead, it loads image requests to dozens of major services — Gmail, YouTube, Reddit, Amazon, GitHub, Slack, PayPal, Twitch, and many more — and watches whether each image loads successfully.
If the image loads, the site assumes you are logged in. If it fails, you are treated as logged out. The result is a list of services split into "logged in" and "not logged in" groups.
Why image loading reveals login state
The trick relies on a quirk of how browsers handle cross-origin images. A page can request an image from another domain and observe whether it loaded, but it cannot read the image contents. Many services redirect unauthenticated users away from certain resources, or serve a different response when a session exists. By requesting a URL that only resolves to a valid image when you are signed in, the test infers your login state without ever touching your session token.
The original research behind this technique comes from the socialmedia-leak project, which documented how "redirect on login" behavior combined with favicon.ico requests could leak authentication status across origins.
Why this matters for your privacy
BrowserLeaks Login: What It Detects and Safer Alternatives - Why this matters for your privacy.
Login state is not trivial information. Knowing which services you use — and which you are actively signed into — lets a third party build a profile of your identity, habits, and affiliations without a single tracking cookie. Combined with other signals, it can help deanonymize you across sites.
The BrowserLeaks page itself flags two related checks alongside the login list:
- Third-party cookies — whether your browser allows them, which enables many cross-site tracking techniques.
- Tracking protection — whether a blocker or browser-level protection is active.
If third-party cookies are allowed and no tracking protection is detected, the login detection test is far more likely to succeed.
The attack surface is broader than social networks
The demo covers dozens of services, but the underlying method applies to any site that exposes a login-dependent resource at a predictable URL. That includes email providers, cloud storage, developer platforms, and payment services. The list on the BrowserLeaks page is illustrative, not exhaustive.
How to check your own exposure
BrowserLeaks Login: What It Detects and Safer Alternatives - How to check your own exposure.
You do not need to be a security researcher to see what your browser reveals. A few minutes of testing will tell you whether your configuration is leaking login state or other identifying signals.
Step 1: Run the login detection test
Visit the BrowserLeaks social page and note the results. If you see services listed as "logged in" that you did not expect, your browser is allowing the cross-origin requests that make this technique work.
Step 2: Check your third-party cookie settings
In most browsers, you can block third-party cookies entirely. This is the single most effective mitigation for this class of attack. Firefox, Safari, and Chromium-based browsers all offer this option, though the exact menu path differs.
Step 3: Verify your tracking protection
Use a content blocker with a maintained filter list. The BrowserLeaks page specifically notes that uBlock Origin with Fanboy's Enhanced Tracking List works well, and that Firefox's built-in Tracking Protection is effective.
Step 4: Test your broader fingerprint
Login detection is only one signal. Your browser also exposes canvas rendering, fonts, screen dimensions, timezone, and dozens of other attributes that combine into a fingerprint. You can run a fingerprint test to see how unique and trackable your browser is, and compare the results before and after changing your settings.
BrowserLeaks vs. BrowserScan: which tool for which job
BrowserLeaks Login: What It Detects and Safer Alternatives - BrowserLeaks vs. BrowserScan: which tool for which job.
Both platforms offer free, browser-based privacy diagnostics, but they emphasize different things.
| Aspect | BrowserLeaks | BrowserScan |
|---|---|---|
| Login detection | Yes, dedicated social login demo | Not the focus |
| Fingerprint analysis | Partial (canvas, WebGL, fonts) | Comprehensive fingerprint detection |
| DNS / WebRTC leak tests | Yes | Yes |
| IP lookup and geolocation | Yes | Yes |
| Port scanning | No | Nmap-powered online port scanner |
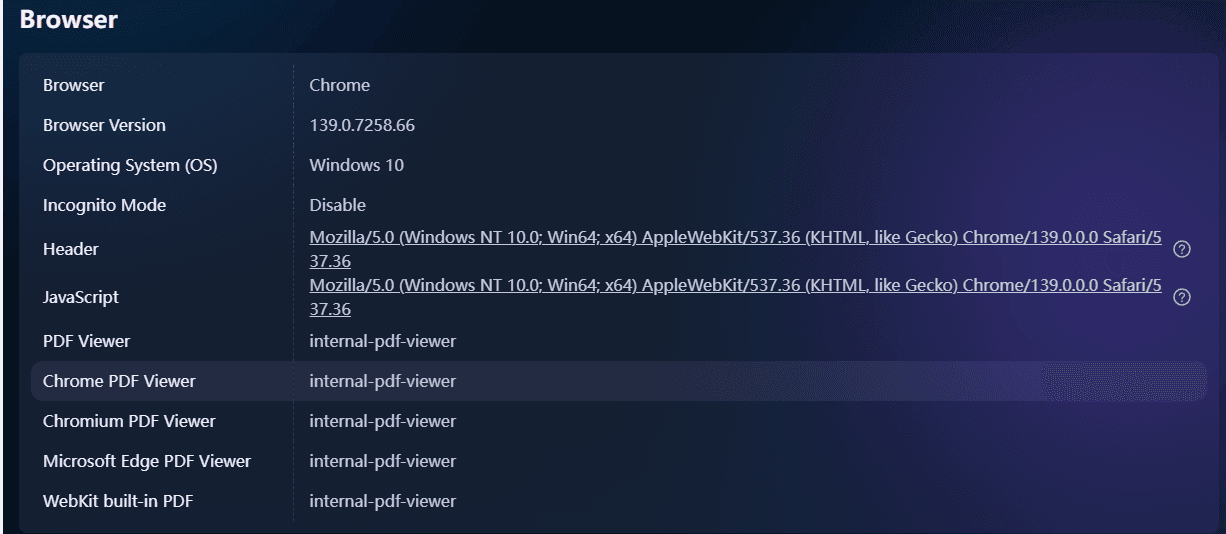
| User agent parsing | Basic header display | Dedicated user agent parser |
| Extra utilities | Limited | 2FA generator, cookie converter, client hints analyzer |
If your goal is specifically to understand cross-origin login detection, BrowserLeaks is the reference implementation. If you want a broader privacy audit — fingerprint uniqueness, leak tests, open ports, and IP intelligence in one place — BrowserScan covers more ground.
When to use each
- Use BrowserLeaks when you want to see the login detection technique in action or check a specific leak vector like DNS or WebRTC.
- Use BrowserScan when you want a consolidated view of your browser fingerprint, network exposure, and connection quality without installing anything.
- Use both if you are hardening a browser profile. The login test tells you about cross-site authentication leaks; the fingerprint test tells you about passive tracking surface.
Practical hardening checklist
- Block third-party cookies in your browser settings.
- Install a content blocker with an active filter list.
- Enable tracking protection at the browser level.
- Run a login detection test to confirm the fix worked.
- Run a fingerprint test to check for other identifying signals.
- Re-test after any browser update, since defaults change.
For a deeper look at how location data can leak even when you think you are protected, see the guide on the Geolocation API and privacy testing.
Related reading
- Geolocation API: How It Works, Privacy Risks & Testing - Learn how the browser Geolocation API works, its accuracy limits, privacy risks, and how to test location leaks with free tools like BrowserScan.
- Nmap Pricing: Is the Network Mapper Really Free? - Nmap pricing explained: the Network Mapper is free and open source. See what's included, how to download it, and how to scan ports without installing anything.
- Data Protection Explained: Principles, Laws, and How to Test Your Own Exposure - Learn what data protection really means, how it differs from data security and privacy, key laws like GDPR and HIPAA, and how to test your own browser and network exposure for free.
Sources and further reading
- My IP Address - The main tools for checking IP address privacy. Showing Your IP Address, Reverse IP Lookup, Hostname, and HTTP Request Headers, Your Country, State, City, ISP/ASN, and Local Lime, Whois Lookup, TCP/IP OS fingerprinting, WebRTC Leak Test, DNS Leak Test, and IPv6 Leak Test.
- DNS Leak Test - The DNS Leak Test is a tool used to determine which DNS servers your browser is using to resolve domain names. This test attempts to resolve 50 randomly generated domain names, of which 25 are IPv4-only and 25 are IPv6-only.
FAQ
Does BrowserLeaks login detection steal my password?
No. The technique does not access credentials or read cookie values. It only observes whether cross-origin image requests succeed or fail, which indirectly reveals login state.
Why does the test show me logged into services I rarely use?
If you have an active session in that browser — even one you forgot about — the test may detect it. Sessions persist until they expire or you sign out.
Can I prevent login detection entirely?
Blocking third-party cookies is the most reliable mitigation. Some browsers also isolate or partition third-party storage by default, which breaks the technique.
Is login detection illegal?
Running the test on your own browser is fine. Using it to probe other users without consent raises legal and ethical issues that vary by jurisdiction.
Does a VPN stop login detection?
No. A VPN changes your IP address, but login detection works at the browser session level. You need cookie and tracking protections, not just a VPN.
What is the difference between login detection and fingerprinting?
Login detection reveals which accounts you are signed into. Fingerprinting identifies your device and browser based on configuration attributes. They are separate signals that can be combined.
How often should I re-test?
After any browser update, extension change, or privacy setting adjustment. Defaults shift between versions, so a configuration that blocked detection last year may not block it today.
Conclusion
BrowserLeaks login detection is a clear demonstration of how much a website can infer about you without asking for anything. The technique is old, well-documented, and still effective when third-party cookies are allowed. The fix is straightforward: block third-party cookies, enable tracking protection, and verify the result with a test. Once login state is locked down, check what else your browser reveals — a fingerprint test is a good next step, and the online port scanner can show whether your network is exposing services you did not intend to share.