
What Is HackerTarget? Tools, Uses & How to Verify Exposure
What Is HackerTarget?
HackerTarget is a hosted collection of open-source security scanners and network intelligence tools. Instead of installing Nmap, OpenVAS, or Nikto on your own machine, you point a web form at a domain or IP address and the scan runs from HackerTarget's servers, returning results in your browser. The platform has been running scans since 2007 and describes itself as a way to help organizations with attack surface discovery and vulnerability identification.
That makes it useful for two very different audiences: security teams mapping what an organization exposes to the internet, and individuals who want to check what their own connection reveals. This article explains what HackerTarget actually does, where it fits in a security workflow, and how to pair its external view with browser-side checks that HackerTarget does not cover.
What HackerTarget Does
HackerTarget's core idea is simple: you cannot defend assets you have not found. Its tools fall into two broad groups.
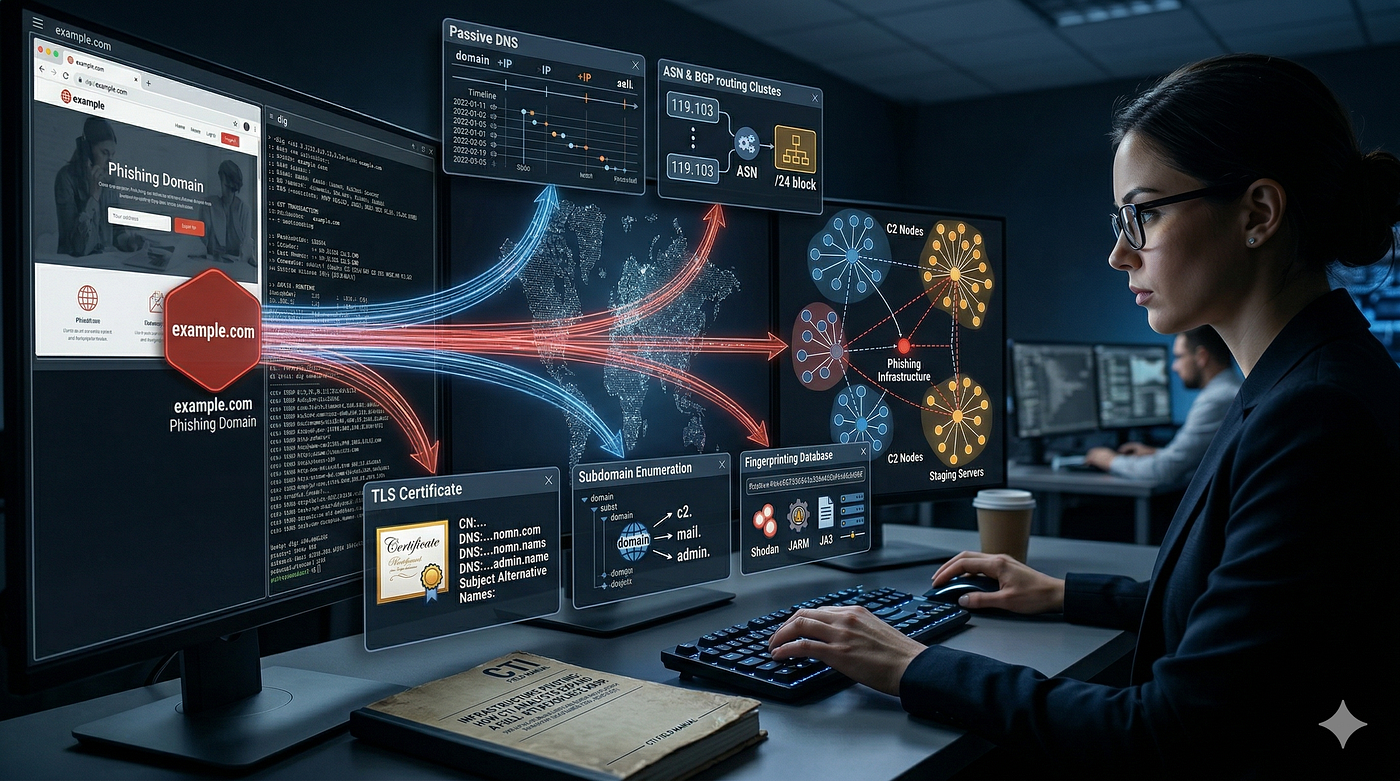
Attack surface discovery
These tools map what is publicly reachable before any vulnerability testing begins:
- Domain and DNS data — subdomain discovery, DNS records, and host information that reveal forgotten or shadow assets.
- Reverse IP lookup — find other domains hosted on the same server, which often exposes shared infrastructure.
- IP location and network data — approximate geolocation, ASN, and netblock context.
- Domain profiler — passive discovery of internet assets tied to an organization.
Vulnerability identification
Once the footprint is known, the hosted scanners probe for weaknesses:
- Nmap port scanner — open ports and listening services, including full port ranges and netblocks.
- OpenVAS — thousands of checks against a host for known vulnerabilities.
- Nikto — web server misconfigurations and vulnerable scripts.
- SSL/TLS scan — weak cipher suites and certificate details.
- CMS scanners — targeted checks for WordPress, Joomla, Drupal, and SharePoint installations.
- WhatWeb / Wappalyzer — technology fingerprinting from headers and page source.
A recurring theme in HackerTarget's own documentation is that no single scanner finds everything. Combining several tools gives a more accurate picture than trusting one result.
Why Hosted Scanning Matters
What Is HackerTarget? Tools, Uses & How to Verify Exposure - Why Hosted Scanning Matters.
Running scans from an external server has practical advantages that show up immediately in real work:
- Attacker's perspective. The scan originates from the internet, not from inside your network, so results reflect what an outsider can actually reach.
- No installation or maintenance. Nothing to patch, no agent to deploy, no local Nmap build to keep current.
- Speed to first result. A form, a target, and a few minutes is often enough to confirm whether a port is exposed.
- Breadth. Different scanners cover different threat categories, which matters when an adversary will try multiple paths.
There are trade-offs. Hosted scans are rate-limited, results are archived by the provider, and you should only scan systems you own or have written permission to test. Scanning third-party infrastructure without authorization is both unethical and, in many jurisdictions, illegal.
HackerTarget vs. Browser-Side Privacy Testing
HackerTarget looks at servers from the outside. It answers questions like "is port 3389 open on this host?" It does not answer "what does my browser reveal about me right now?" Those are different problems, and conflating them leaves gaps.
| Question | HackerTarget | Browser-side testing |
|---|---|---|
| Which ports are open on a server? | Yes | No |
| Which CMS or server software is running? | Yes | No |
| Does my VPN leak my real IP? | No | Yes |
| What is my browser fingerprint? | No | Yes |
| What does my user agent expose? | No | Yes |
| Is my DNS resolving through my ISP? | No | Yes |
If you use a VPN and want to confirm it is actually working, a port scanner will not tell you. You need leak tests and fingerprint analysis that run in your own browser. BrowserScan offers free, web-based checks for exactly that: DNS and WebRTC leak tests, browser fingerprint analysis, IP address lookup with proxy detection, and a user agent parser. It requires no installation and complements the server-side view HackerTarget provides.
A practical workflow looks like this:
- Use HackerTarget to map your external footprint and find exposed services.
- Fix or firewall anything that should not be public.
- Use browser-side tools to confirm your own connection is not leaking your real IP or a unique fingerprint.
- Re-test after changes to verify the fix held.
Using HackerTarget Tools and the API
What Is HackerTarget? Tools, Uses & How to Verify Exposure - Using HackerTarget Tools and the API.
Most HackerTarget tools are available through the web interface, and many are also exposed through a documented API that returns plain text or JSON. That makes them scriptable for monitoring.
A typical API call for a host lookup looks like:
https://api.hackertarget.com/hostsearch/?q=example.com
And a port scan request:
https://api.hackertarget.com/nmap/?q=example.com
Free API usage is rate-limited, so batch jobs need throttling. For heavier or scheduled scanning, HackerTarget offers membership and enterprise plans with higher limits. If you are comparing costs across privacy and security tools, our breakdown of BrowserScan pricing explains which checks stay free and where paid tiers begin.
Common Use Cases
- Penetration testing reconnaissance. Information gathering is the first phase of any assessment, and HackerTarget automates much of it.
- Continuous monitoring. Scheduled scans catch newly opened ports or expired certificates before an attacker does.
- Bug bounty triage. Quick footprint checks help you decide whether a target is worth deeper investigation.
- Personal exposure checks. Individuals can see what their home IP or small business domain reveals publicly.
- VPN and privacy verification. Pair server-side scans with browser leak tests to cover both sides of your exposure.
If your concern is specifically about what your browser leaks, our guide to secure browsing in 2026 walks through the leak vectors that port scanners never see.
Limitations to Keep in Mind
- Authorization is required. Only scan assets you own or have explicit permission to test.
- Results are point-in-time. A clean scan today does not mean a clean scan tomorrow.
- False positives and negatives exist. Cross-check findings with a second tool before acting.
- No browser-layer visibility. Fingerprints, cookies, WebRTC, and DNS leaks are outside its scope.
- Rate limits apply. Free API calls are capped, which matters for automation.
Related reading
- Mozilla VPN Tutorial: Setup, Servers & Leak Checks - Step-by-step Mozilla VPN tutorial: install on Windows, Mac, Android, iOS and Linux, pick servers, use multi-hop, and verify your IP with free leak tests.
- IP-Lookup.net: What It Shows and How to Use It Safely - IP-Lookup.net reveals IP location, ISP, ASN, and proxy signals. Learn what it shows, its limits, and how to verify leaks with BrowserScan.
- Chameleon Mode Setup: Install, Profiles & Proxy Guide - Step-by-step Chameleon Mode setup for Windows and Mac: install, create isolated profiles, add proxies, and verify your fingerprint with free tests.
Sources and further reading
- About | HackerTarget.com - Online open source security to test the security of Internet connected systems. Port scanning, SQL Injection and Information gathering are just a start.
- 28 Online Vulnerability Scanners & Network Tools - Online Vulnerability Scanners to Identify Vulnerabilities and Map the Attack Surface. 28 Trusted Security Scanners and Free Network Tools.
- HackerTarget ToolKit Tools To Help Organizations With Attack Surface Discovery - Information Gathering is an important part of Penetration Testing of web applications or any network application. Collecting more information about the target can help the attacker to easily gain access to the target domain server. HackerTarget is a python-based tool that is fully automated for Information Gathering. This tool can
FAQ
Is HackerTarget free?
Many tools and API endpoints are free with rate limits. Higher-volume scanning, scheduling, and broader asset coverage require a membership or enterprise plan.
Is HackerTarget legal to use?
Using it against systems you own or have written authorization to test is legal. Scanning third-party systems without permission can violate computer misuse laws.
Does HackerTarget install anything on my machine?
No. It is a hosted service. You interact through a web form or API, and scans run from HackerTarget's servers.
Can HackerTarget tell me if my VPN is leaking?
No. VPN leaks happen in your browser and network stack, not on the target server. Use a dedicated leak test for that.
What is the difference between HackerTarget and a browser fingerprint test?
HackerTarget scans servers from the outside. A fingerprint test examines what your own browser reveals to every site you visit, including canvas, WebGL, fonts, and user agent data.
Can I automate HackerTarget scans?
Yes, through its API. Free tiers are rate-limited, so production monitoring usually needs a paid plan or careful throttling.
Conclusion
HackerTarget is best understood as an external reconnaissance and vulnerability scanning platform. It maps what an organization exposes to the internet and probes that surface with trusted open-source tools, all without local installation. It is genuinely useful for penetration testers, IT teams, and anyone who wants to know what their public-facing infrastructure looks like from the outside.
What it does not do is inspect your browser. If your goal is privacy rather than server hardening, the two concerns overlap but do not replace each other. Start with HackerTarget to understand your external footprint, then verify your own connection with browser-based leak and fingerprint tests so both sides of your exposure are covered.