
Browser Fingerprinting: How It Works and How to Test Yours
Browser Fingerprinting: How It Works and How to Test Yours
Browser fingerprinting is one of the most persistent ways websites and tracking companies recognize you online. Unlike cookies, it does not require anything to be stored on your device. Instead, it quietly assembles dozens of ordinary details about your browser, operating system, and hardware into a profile that can be startlingly unique. This article explains how fingerprinting works, the techniques behind it, the privacy trade-offs, and how you can test your own browser to see what trackers see.
What Is Browser Fingerprinting?
Browser Fingerprinting: How It Works and How to Test Yours - What Is Browser Fingerprinting?.
Browser fingerprinting is the systematic collection of information about a remote browser or device for identification purposes. When you visit a website, scripts can read a wide range of attributes: your browser type and version, operating system, screen resolution, installed fonts, time zone, language settings, and more. Individually, each signal is weak. Combined, they often form an identifier unique enough to distinguish you from millions of other visitors.
The result is sometimes called a "digital fingerprint" or "device fingerprint." It stays relatively stable across browsing sessions and works even in incognito mode, after clearing cookies, or when third-party cookies are blocked. That persistence is what makes fingerprinting attractive to fraud-prevention platforms and concerning to privacy advocates.
How Browser Fingerprinting Works
Browser Fingerprinting: How It Works and How to Test Yours - How Browser Fingerprinting Works.
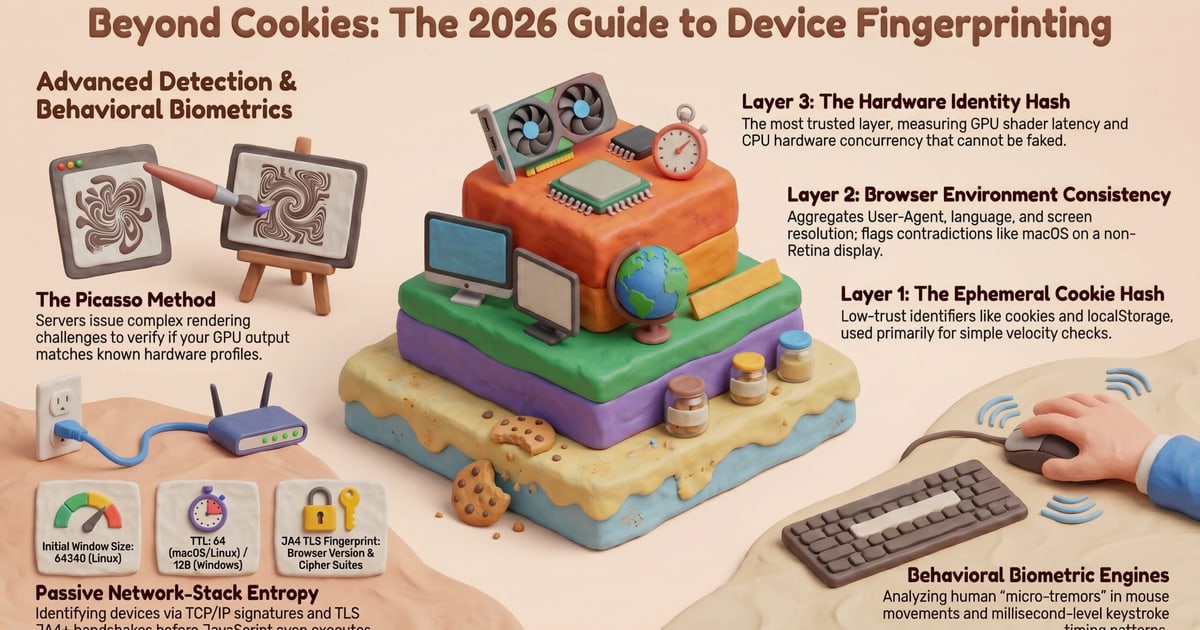
Fingerprinting operates on two principles: entropy and persistence.
- Entropy measures how much identifying information a set of signals contains. A single data point such as "Chrome on Windows" is shared by millions of people. But adding your exact browser build, screen dimensions, installed fonts, graphics card rendering behavior, and keyboard layout narrows the field dramatically.
- Persistence means the identifier should survive small changes. A good fingerprinting system weighs signals by their durability. If you update one font but keep the same hardware and time zone, the fingerprint should still recognize you.
Scripts run in the background when a page loads. They do not alter your experience or require permission. The collected attributes are hashed into a visitor ID that can be compared across visits and, in some cases, across websites.
Common Browser Fingerprinting Techniques
Browser Fingerprinting: How It Works and How to Test Yours - Common Browser Fingerprinting Techniques.
Several techniques are widely used to gather high-entropy signals. Understanding them makes it easier to interpret the results of a fingerprint test.
1. Canvas Fingerprinting
Canvas fingerprinting draws a hidden image or text string using the HTML5 canvas element, then reads back the rendered pixels. Because rendering depends on the graphics card, GPU drivers, operating system, and browser, the output differs subtly between machines. The resulting hash is a strong hardware-related signal.
2. WebGL Fingerprinting
WebGL exposes information about the GPU and its driver. A script can query the renderer and vendor strings, then run a rendering test similar to canvas fingerprinting. This technique often reveals the exact graphics hardware model and driver version.
3. Font Detection
Your system's installed fonts are surprisingly identifying. A script can check whether hundreds of common and uncommon fonts are present. The combination of available fonts varies enough between users to serve as a reliable fingerprint component.
4. AudioContext Fingerprinting
Audio fingerprinting processes an inaudible sound through the browser's audio stack and measures how the hardware and software alter the waveform. Differences in sound cards, drivers, and browser implementations produce a unique signature.
5. Screen and Window Properties
Screen resolution, color depth, device pixel ratio, and the size of the browser window all contribute to the fingerprint. On mobile devices, these values are often tied closely to a specific model.
6. API and Header Analysis
HTTP headers such as User-Agent, Accept-Language, and Accept-Encoding reveal browser and locale details. JavaScript APIs expose additional information, including time zone, platform, touch support, and installed plugins. Client hints are a newer mechanism that lets servers request specific device details directly.
Fingerprinting vs. Cookies
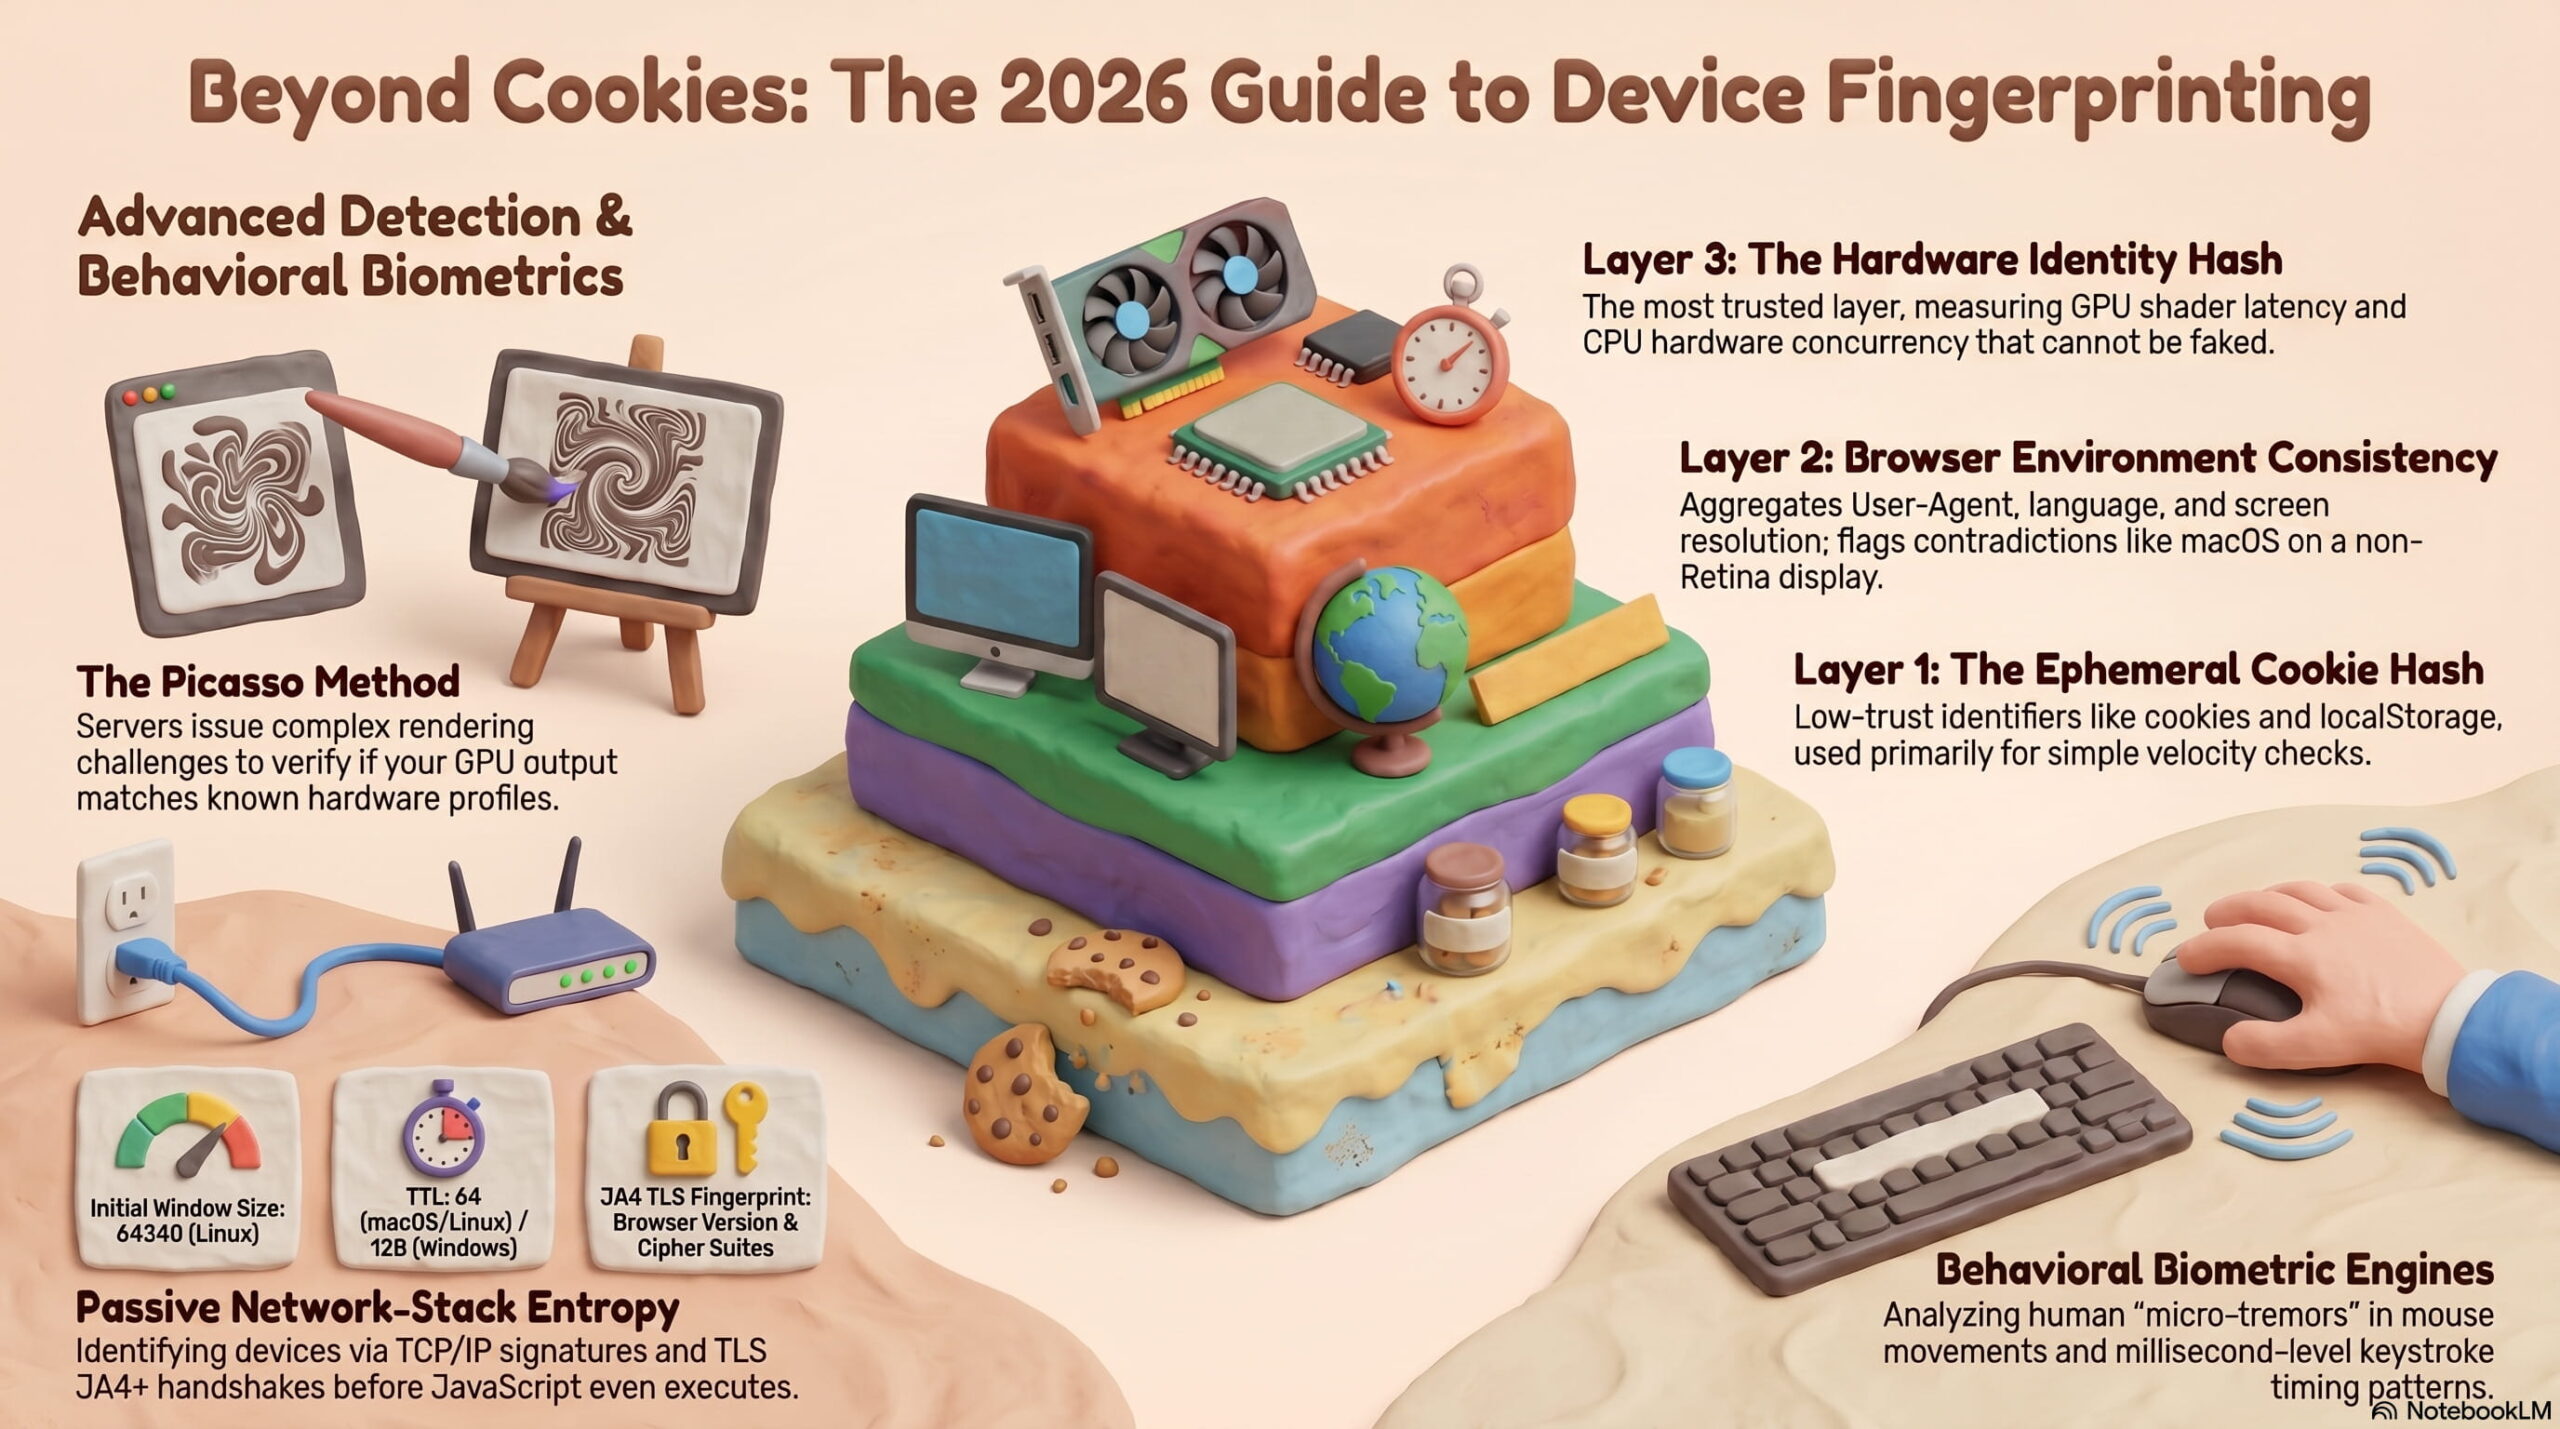
Browser Fingerprinting: How It Works and How to Test Yours - Fingerprinting vs. Cookies.
Cookies and fingerprinting solve the same problem differently.
| Feature | Cookies | Browser Fingerprinting |
|---|---|---|
| Storage location | Stored on the user's device | No storage required |
| User control | Can be blocked or cleared easily | Hard to block or clear |
| Works in incognito mode | Usually not | Yes |
| Persistence | Lost when cleared | Survives most cleanup |
| Consent visibility | Often shown in cookie banners | Usually invisible to users |
Cookies are explicit: a small file is placed in your browser, and you can inspect or delete it. Fingerprints are implicit: they are computed from properties you expose simply by loading a page. That is why fingerprinting feels more invasive even when it is used for legitimate security purposes.
Why Websites Use Browser Fingerprinting
Fingerprinting is not only a tracking tool. It underpins many fraud-prevention and security systems.
- Account takeover prevention: If a login attempt comes from a browser fingerprint that has never been associated with the account, the system can require additional verification.
- Payment fraud detection: E-commerce platforms use fingerprints to spot repeat fraudsters who clear cookies or switch accounts.
- Bot and scraper mitigation: Automated traffic often has inconsistent or missing browser signals. Fingerprinting helps separate bots from humans.
- Session consistency: Some services use fingerprints to detect session hijacking when a cookie is stolen and used from a different browser.
Under regulations such as GDPR and CCPA, using fingerprinting for security and fraud prevention may qualify as a legitimate interest. Using it for ad targeting or cross-site behavioral profiling generally requires consent and disclosure.
Privacy Risks of Browser Fingerprinting
The same technology that stops fraud can enable surveillance. Because fingerprints do not require consent banners or stored files, users often have no idea they are being fingerprinted. When a fingerprint is shared across many websites through a common tracking script, it becomes a cross-site identifier that follows you around the web.
This creates several concerns:
- Invisible tracking: Users cannot easily see or delete a fingerprint the way they can clear cookies.
- Cross-site profiling: A stable fingerprint lets data brokers link your visits across unrelated sites.
- Reduced anonymity: Even privacy tools like VPNs do not hide browser fingerprints. A VPN changes your IP address, but your fingerprint may remain the same, allowing trackers to reconnect your sessions.
- Discriminatory practices: Fingerprints can be used for price discrimination, targeted scams, or excluding certain device types from content.
Privacy-focused browsers such as Tor and Brave include built-in countermeasures. Tor standardizes many browser properties across users to make everyone look similar, while Brave blocks known fingerprinting scripts and offers fingerprinting protection modes.
How to Test Your Browser Fingerprint
Testing is the first step to understanding your exposure. A good fingerprint test shows which signals are visible, how unique they are, and whether your privacy tools are working.
Free testing tools such as the EFF's Cover Your Tracks and the academic project AmIUnique analyze your browser and report whether your fingerprint is unique among their datasets. These tests are useful for a one-time check, but they do not always show the full picture for VPN users or people testing specific leak vectors.
For a more complete diagnostic, BrowserScan offers a suite of free, browser-based privacy tests in one place. Its browser fingerprint analysis verifies how authentic and unique your fingerprint appears, while its DNS and WebRTC leak tests check whether your VPN is accidentally exposing your real IP address. The platform also includes an IP lookup with geolocation and proxy detection, a port scanner, and a user agent parser. Because everything runs in the browser without installation, it is a practical way to audit your setup before and after changing privacy settings.
When you run a fingerprint test, pay attention to three things:
- Uniqueness: Does the tool say your fingerprint is unique or shared with many others?
- Stability: Does your fingerprint stay the same across visits, or does it change unpredictably?
- Leak signals: Are your real IP, time zone, or language exposed despite using a VPN or proxy?
How to Reduce Browser Fingerprinting
Complete fingerprint protection is difficult because browsers must expose some information to function. However, you can reduce your uniqueness and make tracking less reliable.
Use a Privacy-Hardened Browser
Tor Browser is the strongest option because it intentionally makes all users look as similar as possible. Brave and Firefox with strict privacy settings also block many fingerprinting scripts and randomize certain signals.
Install Fingerprint-Blocking Extensions
Extensions such as privacy-focused content blockers can stop known fingerprinting scripts from loading. Some browser add-ons also spoof or randomize canvas, WebGL, and font data. Be aware that aggressive spoofing can break websites and may itself be detectable.
Keep Your Browser Updated
Updates patch known fingerprinting bypasses and improve built-in protections. An outdated browser often has a more distinctive fingerprint because it differs from the current mainstream version.
Limit Installed Fonts and Plugins
Every additional font or plugin increases entropy. Removing rarely used fonts and disabling unnecessary plugins reduces the number of signals a tracker can collect.
Combine with a VPN — and Verify It
A VPN hides your IP address but does not change your browser fingerprint. To prevent trackers from linking your sessions, you need both network-level privacy and browser-level fingerprint protection. After connecting to a VPN, run a DNS and WebRTC leak test to confirm your real IP is not exposed. A fingerprint that stays identical across different VPN servers can still be used to recognize you.
Test After Every Change
Privacy settings interact in unpredictable ways. After changing browsers, installing extensions, or adjusting VPN settings, run a fingerprint test again. Compare the results to see whether your uniqueness decreased or whether a new setting introduced a leak.
For a step-by-step approach to combining these measures, see our guide on building a realistic digital privacy plan.
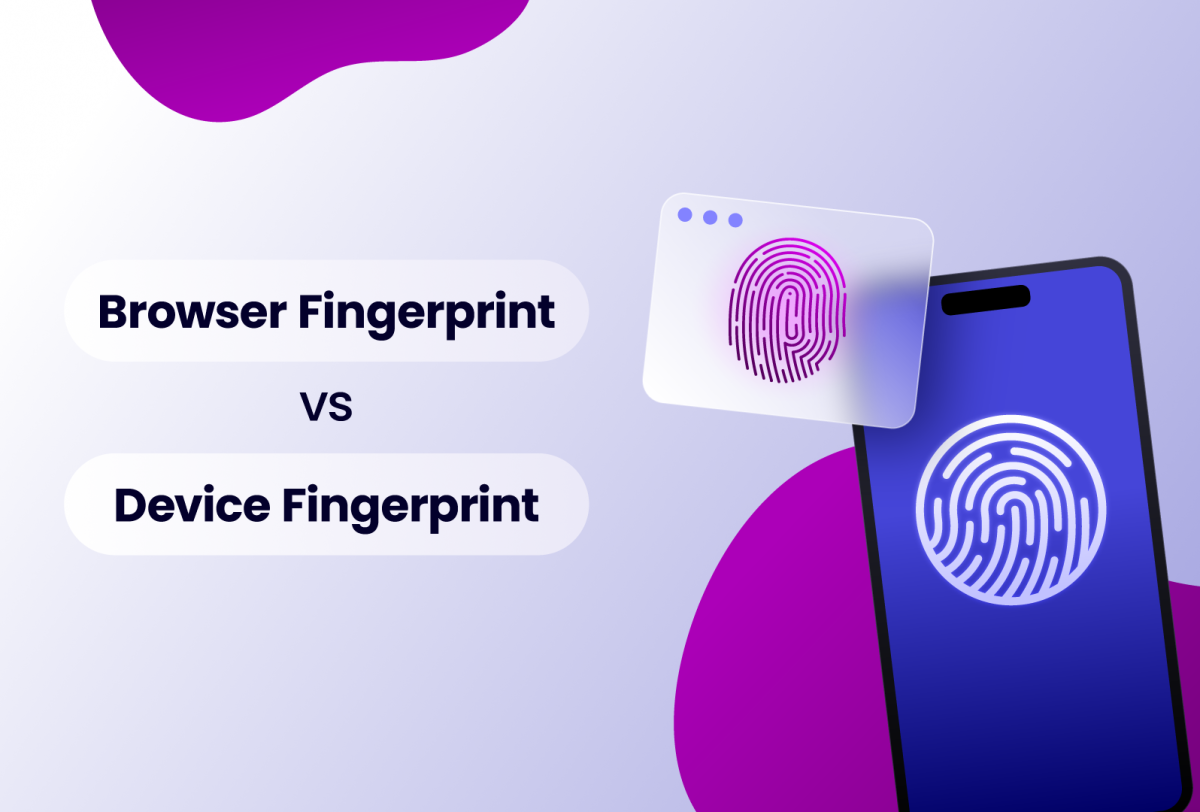
Browser Fingerprinting vs. Device Fingerprinting
Although the terms are often used interchangeably, they refer to different scopes.
- Browser fingerprinting identifies a specific browser installation. The same device can have multiple browser fingerprints if it runs Chrome, Firefox, and Edge.
- Device fingerprinting aims to identify the physical device regardless of which browser or app is used. It is more common in mobile apps, where signals such as hardware identifiers, sensor data, and OS-level properties are available.
Device fingerprinting is generally more invasive because it can survive browser changes and app reinstalls. Browser fingerprinting is more common on the open web because it requires only JavaScript and HTTP headers.
Related reading
- What Is IPsec? How IPsec VPNs Secure Your Traffic - Learn how IPsec works, the difference between AH and ESP, tunnel vs transport mode, IKE key exchange, and how to test your IPsec VPN for leaks.
- TLS Fingerprint Preservation: What It Is and How It Works - Learn what TLS fingerprint preservation is, how JA3, JA4, and JARM work, why preserving fingerprints matters for privacy and automation, and how to test yours.
Frequently Asked Questions
Is browser fingerprinting legal?
In most jurisdictions, fingerprinting itself is not illegal. What matters is how it is used. Under GDPR and CCPA, using fingerprints for security and fraud prevention may be allowed as a legitimate interest, while using them for ad tracking or profiling generally requires consent and disclosure.
Can a VPN prevent browser fingerprinting?
No. A VPN hides your IP address and encrypts your traffic, but your browser still exposes the same fingerprint signals. A determined tracker can link your sessions across different IP addresses using your fingerprint. Use a VPN together with fingerprint-reducing browser settings.
Does incognito or private browsing mode stop fingerprinting?
No. Private browsing prevents local storage such as cookies and history from persisting, but it does not block fingerprinting scripts. Your fingerprint in incognito mode is often nearly identical to your normal browsing fingerprint.
How accurate is browser fingerprinting?
Accuracy depends on the number and quality of signals collected. Research projects such as AmIUnique have found that a large majority of browsers have unique or nearly unique fingerprints. Commercial systems that combine fingerprinting with machine learning can achieve very high identification rates, especially when fingerprints are tracked over time.
Can I completely block browser fingerprinting?
Complete blocking is difficult because browsers must reveal some information to render web pages correctly. The most effective approach is to reduce uniqueness by using a privacy-hardened browser such as Tor, limiting installed fonts and plugins, and blocking known fingerprinting scripts. Even then, some residual signals remain.
What is the difference between canvas and WebGL fingerprinting?
Both are rendering-based techniques. Canvas fingerprinting draws 2D content and reads back the pixels, while WebGL fingerprinting uses 3D graphics rendering and can also query GPU vendor and renderer strings. WebGL often reveals more specific hardware information.
Conclusion
Browser fingerprinting is a double-edged technology. It powers fraud prevention, account security, and bot detection, but it also enables invisible cross-site tracking that most users never notice. Because fingerprints do not rely on cookies, they survive incognito mode, cookie clearing, and even VPN connections.
The most practical response is not to panic but to measure. Run a fingerprint test to see how unique your browser is, then make targeted changes: switch to a privacy-hardened browser, limit fonts and plugins, and verify that your VPN is not leaking identifying data. Tools like BrowserScan make this easy by combining fingerprint analysis, DNS and WebRTC leak tests, and IP diagnostics in one browser-based platform. For deeper background on the techniques behind fingerprinting, the Fingerprint blog provides a useful technical overview.
Fingerprinting is unlikely to disappear, but informed users can reduce their exposure. Understanding what trackers see is the first step toward controlling it.