
TLS Fingerprint Preservation: What It Is and How It Works
TLS Fingerprint Preservation: What It Is and How It Works
Every time your browser or application opens a secure HTTPS connection, it sends a TLS handshake that reveals more than you might expect. The exact combination of cipher suites, extensions, and supported parameters in that handshake forms a fingerprint that can identify your client, flag automation, or expose a mismatch between your claimed browser and your actual TLS behavior. TLS fingerprint preservation is the practice of keeping that fingerprint consistent, legitimate, and aligned with the client you want to appear as.
This matters for two very different audiences. Security teams use TLS fingerprints to detect bots, block scraping, and stop credential-stuffing attacks. Privacy-conscious users, automation developers, and anti-detect browser users work to preserve a convincing fingerprint so their traffic blends in with normal browser traffic. Understanding both sides is the key to making informed decisions about your own setup.
What Is a TLS Fingerprint?
TLS Fingerprint Preservation: What It Is and How It Works - What Is a TLS Fingerprint?.
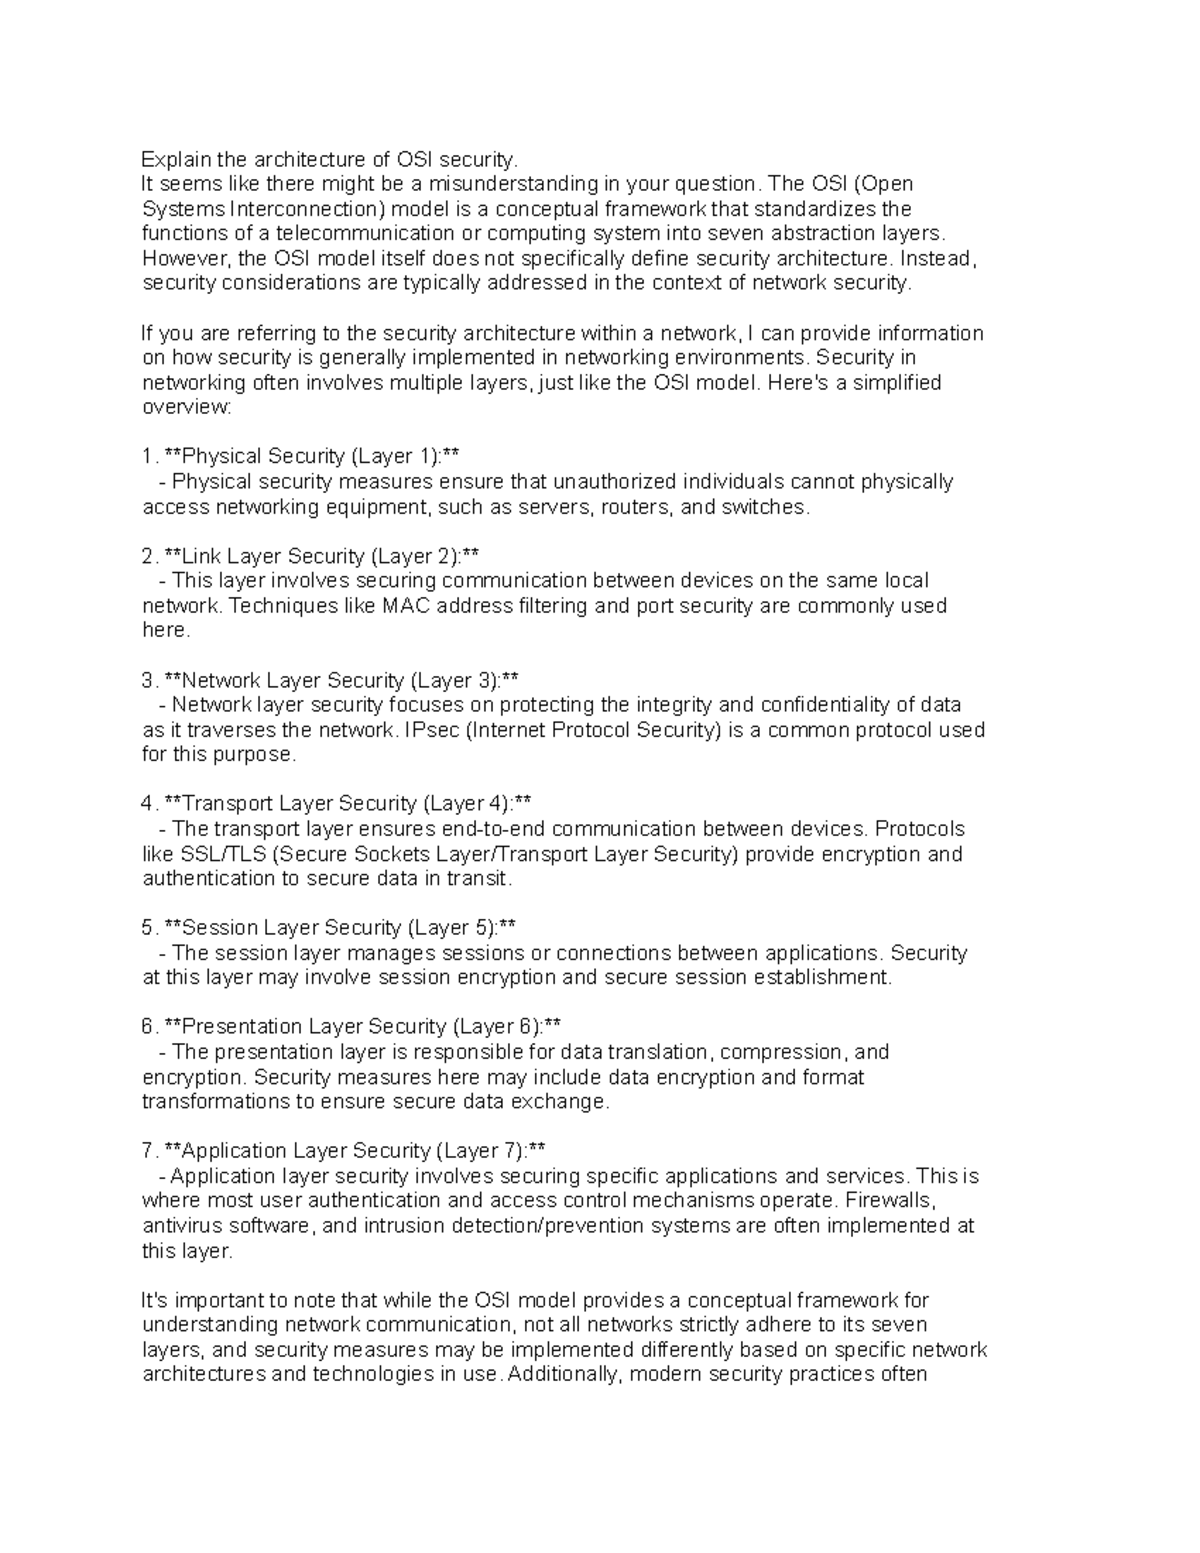
A TLS fingerprint is a derived identifier based on the observable characteristics of the Transport Layer Security handshake between a client and a server. Because the initial ClientHello message is sent in plaintext before encryption begins, anyone observing the connection can inspect its structure.
The ClientHello contains several fields that vary by implementation:
- Supported TLS versions
- The ordered list of cipher suites
- Compression methods
- TLS extensions and their specific values
- Supported elliptic curve groups and point formats
Different TLS libraries construct this message differently. Firefox uses NSS, Chrome uses BoringSSL, Safari relies on Apple's Secure Transport, and Windows applications often use SChannel. Each library has its own defaults, ordering conventions, and extension behavior. These differences are stable enough that a server can often identify the client family, and sometimes the specific version, just from the handshake.
A crucial point: a TLS fingerprint is usually not unique to an individual user. Many Chrome users on the same version share the same fingerprint. That is exactly what makes preservation useful. You do not need a one-of-a-kind signature; you need a signature that matches a large, legitimate population.
How TLS Fingerprinting Works in Practice
TLS Fingerprint Preservation: What It Is and How It Works - How TLS Fingerprinting Works in Practice.
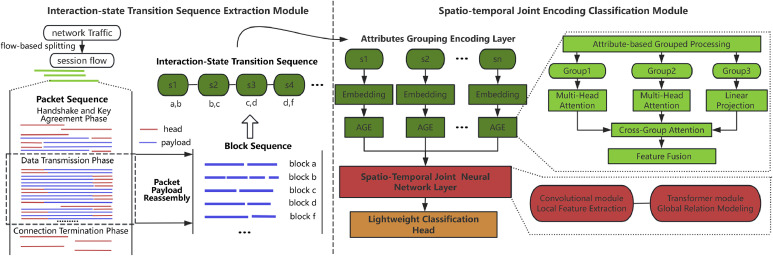
When a client connects to a server, the server or a passive observer records the ClientHello and extracts a defined set of fields. Those fields are normalized, concatenated, and hashed to produce a compact identifier. The server then compares that identifier against known profiles.
If the hash matches a known Chrome profile, the connection looks like Chrome. If it matches a known Python requests library profile, the connection looks like a script. If a client claims to be Chrome in its User-Agent but presents a Python TLS fingerprint, that mismatch is a strong signal of automation or spoofing.
This is why TLS fingerprinting has become a standard layer in bot mitigation stacks. It complements cookie-based tracking and browser fingerprinting by catching what those techniques miss: the network-level truth of how the client actually speaks TLS.
Common TLS Fingerprinting Techniques
Three methods dominate the field, and each answers a different question.
JA3 is the oldest widely adopted client fingerprinting method, introduced by Salesforce researchers in 2017. It builds an MD5 hash from the TLS version, cipher suite list, extensions, supported groups, and elliptic curve formats in the ClientHello. JA3 is simple, fast, and well-supported across security tools. Its main weakness is that it can produce false positives when different clients happen to share the same observable parameters, and it can be spoofed by deliberately mimicking a target fingerprint.
JA4 is a newer evolution designed to address JA3 limitations. It incorporates additional handshake details and uses a different hashing approach to produce a more granular and stable identifier. JA4 is increasingly preferred in environments where sophisticated bot detection is required, because it is harder to spoof through simple parameter reordering.
JARM takes a different approach. Instead of passively observing a client, JARM actively probes a server by sending ten specially crafted ClientHello messages and hashing the server's responses. This produces a server-side fingerprint that helps identify command-and-control infrastructure, malware servers, and other suspicious endpoints. JARM is a threat-intelligence tool rather than a client-identification tool.
What Does TLS Fingerprint Preservation Mean?
TLS Fingerprint Preservation: What It Is and How It Works - What Does TLS Fingerprint Preservation Mean?.
Preservation means keeping the TLS fingerprint of your traffic consistent with the identity you are presenting. In practical terms, it involves two goals:
- Consistency across requests. If your first request looks like Chrome 120 and your second looks like a generic TLS library, that inconsistency itself is a detection signal.
- Alignment with your declared client. If your HTTP headers say Chrome but your TLS handshake says Python, the mismatch is immediately suspicious.
For automation developers, preservation often means configuring the TLS layer of their HTTP client to replicate the exact ClientHello of a real browser. For anti-detect browser users, it means ensuring the browser's underlying network stack does not leak a fingerprint that contradicts the spoofed browser profile.
Preservation is not the same as hiding. You cannot make a TLS handshake invisible, because the ClientHello must be readable for the connection to be established. What you can do is make it look like something ordinary.
Why TLS Fingerprint Preservation Matters
TLS Fingerprint Preservation: What It Is and How It Works - Why TLS Fingerprint Preservation Matters.
For Bot Detection and Fraud Prevention
Security teams rely on TLS fingerprints to separate humans from scripts. Credential-stuffing tools, scraping frameworks, and account-checking bots often use standard HTTP libraries with distinctive fingerprints. Blocking those fingerprints stops a large volume of automated abuse before it reaches the application layer.
Web Application Firewalls and bot management platforms increasingly incorporate JA3 or JA4 rules. A request from an outdated or non-standard TLS client can be challenged, rate-limited, or dropped entirely, even if the HTTP headers look perfect.
For Privacy and Automation Users
On the other side, anyone running automation, using a privacy-focused browser, or managing multiple accounts needs to understand that TLS fingerprints can expose their activity. A scraper that sends perfect headers but a default Python TLS handshake is easy to identify. A privacy browser that claims to be Firefox but presents a Chromium TLS profile is equally suspicious.
Preserving a legitimate TLS fingerprint reduces the chance of being flagged as automated traffic. It also reduces the risk of being fingerprinted as a unique, trackable client when your goal is to blend into a crowd.
How to Check and Preserve Your TLS Fingerprint
Before you can preserve a fingerprint, you need to know what your current setup is actually sending. A browser fingerprint analysis tool can show you the observable parameters of your connection, including whether your TLS profile matches your declared browser. This kind of check is especially useful after changing VPNs, proxies, or browser configurations, because any of those changes can alter your TLS behavior.
BrowserScan offers a free, web-based browser fingerprint analysis that reports on the characteristics your browser exposes, helping you verify whether your setup looks consistent and authentic. For users who want to go deeper into network-level verification, the platform also provides DNS and WebRTC leak tests to confirm that a VPN is not exposing your real IP address, plus an IP address lookup with geolocation and proxy detection. These checks complement TLS fingerprint testing by confirming that every layer of your connection tells the same story.
For a practical testing workflow, combine a TLS fingerprint check with a broader privacy audit. Tools like BrowserLeaks let you inspect multiple fingerprint vectors in one place, and a guide on how to use BrowserLeaks can walk you through the process step by step.
Practical Steps for Preservation
If your goal is to preserve a convincing TLS fingerprint, consider these approaches:
- Use a real browser engine. The most reliable way to match a legitimate fingerprint is to actually use the browser you claim to be. Headless Chrome driven by a real browser binary produces a far more authentic TLS profile than a raw HTTP library.
- Configure your HTTP client carefully. If you must use a library like Python requests or Node.js fetch, use a TLS configuration that replicates a known browser's cipher suite order and extensions. Several open-source projects provide pre-built JA3/JA4 impersonation profiles.
- Avoid mixing client signals. Keep your User-Agent, HTTP/2 fingerprint, TLS fingerprint, and JavaScript-exposed browser properties aligned. A single mismatch can undo the work of preserving everything else.
- Test after every change. Proxy changes, library upgrades, and browser updates can all alter your TLS fingerprint. Re-test after any modification to confirm the fingerprint still matches your target profile.
TLS Fingerprint Preservation vs. Browser Fingerprinting
TLS fingerprinting and browser fingerprinting operate at different layers, and they answer different questions.
| Aspect | TLS Fingerprinting | Browser Fingerprinting |
|---|---|---|
| Layer | Network transport | Application and JavaScript |
| Data source | ClientHello message |
Canvas, fonts, WebGL, headers, screen metrics |
| Visibility | Visible to any observer of the connection | Requires JavaScript execution in the page |
| Uniqueness | Shared by many clients of the same type | Often unique or near-unique to an individual |
| Primary use | Bot detection, protocol-level identification | User tracking, fraud prevention |
A complete anti-detection or privacy strategy must address both. Preserving a valid TLS fingerprint prevents network-level flagging, while managing browser fingerprint entropy prevents application-level tracking. Neither alone is sufficient.
Limitations and Realities of TLS Fingerprint Preservation
Preservation is not a silver bullet. Several limitations are worth understanding before you invest effort in it.
First, fingerprints drift. Browser vendors update their TLS libraries regularly, and a fingerprint that matches Chrome today may not match Chrome next month. Automation tools must update their impersonation profiles continuously to keep pace.
Second, advanced detection systems use more than the static ClientHello hash. Some observe how the client responds to unusual server inputs, a technique explored in academic research on two-step TLS-based browser fingerprinting. This behavioral layer is harder to spoof than a static parameter list.
Third, preservation can backfire if done poorly. A fingerprint that matches a known bot profile is worse than no fingerprint management at all. The goal is always to match a large, legitimate population, not to create a unique or exotic signature.
Finally, TLS fingerprinting is one signal among many. Bot detection systems combine it with IP reputation, behavioral analysis, HTTP/2 fingerprints, and JavaScript challenges. Preserving a TLS fingerprint helps, but it does not make traffic invisible.
Related reading
- Penetration Testing Tools: Types, Top Picks & How to Choose - Explore the best penetration testing tools by category, from Nmap and Burp Suite to Kali Linux. Learn how to choose, combine, and verify your pentest setup.
- Network Security Tools: 15 Essential Types & How to Use Them - Discover the essential network security tools for monitoring, scanning, and defending your systems. Compare free and paid options and learn how to verify your setup.
- Algo VPN Tutorial: Deploy a Personal WireGuard & IPsec VPN - Step-by-step Algo VPN tutorial covering cloud deployment, client setup, user management, and leak testing to verify your personal VPN works.
Sources and further reading
- Applications of TLS Fingerprinting in Bot Mitigation - CDNetworks - Sep 12, 2024 ... While TLS fingerprinting can effectively detect bot traffic, it also has certain limitations. As attackers continuously upgrade and change their ...
- TLS Fingerprinting: Techniques and Bypassing Methods - Nstbrowser - Nstbrowser is a powerful anti-detect browser designed for multi-accounting professionals to manage multiple accounts securely and efficiently. Try it now for free!
FAQ
What is the difference between JA3 and JA4?
JA3 hashes a fixed set of ClientHello fields using MD5 and was introduced in 2017. JA4 is a newer method that incorporates additional handshake parameters and uses a different hashing approach, producing a more granular and harder-to-spoof fingerprint. JA4 is increasingly favored for high-assurance bot detection.
Can a VPN change my TLS fingerprint?
A VPN changes your IP address and network path, but it does not directly change your TLS handshake. However, if your VPN client routes traffic through a proxy that terminates and re-establishes TLS, the fingerprint seen by the destination server may change. Testing after connecting to a VPN is always recommended.
Is TLS fingerprint preservation legal?
Preserving or modifying your own TLS fingerprint is generally legal. The legality of the activity you perform with that preserved fingerprint is a separate question. Web scraping, automation, and multi-accounting are subject to terms of service and applicable laws, regardless of how your TLS handshake looks.
How can I test my current TLS fingerprint?
You can use a browser fingerprint analysis tool to inspect your connection's observable parameters, including TLS-related characteristics. For a more targeted check, several online services display your JA3 or JA4 hash directly. Combine this with DNS and WebRTC leak tests to verify that your entire connection profile is consistent.
Does TLS fingerprinting work with HTTP/3 and QUIC?
HTTP/3 uses QUIC instead of TLS over TCP, which changes the handshake structure. QUIC has its own fingerprinting surface, and detection tools are evolving to analyze QUIC ClientHello messages alongside traditional TLS. Preservation strategies must eventually account for both protocols.
Conclusion
TLS fingerprint preservation sits at the intersection of security and privacy. For defenders, it is a reliable signal for separating humans from bots. For privacy-conscious users and automation developers, it is a requirement for blending into legitimate traffic. The core principle is simple: your TLS handshake should match the client you claim to be, consistently, across every request.
Start by testing what your current setup actually exposes. Verify that your TLS fingerprint aligns with your declared browser, that your VPN is not leaking identifying information, and that your IP address does not contradict your intended profile. Then maintain that alignment as your tools and browsers evolve. In a detection landscape that grows more sophisticated every year, a preserved and consistent TLS fingerprint is one of the most practical steps you can take to keep your traffic looking ordinary.