
Proxy Detection: How It Works, Methods & Free Tools
Proxy Detection: How It Works, Methods, and Free Tools
Proxy detection is the process of determining whether an IP address belongs to a proxy server, VPN, Tor exit node, or other anonymizing service rather than a regular residential or business connection. Fraud teams, streaming platforms, e-commerce sites, and security engineers use proxy detection to block abuse, prevent account takeovers, and enforce regional restrictions. This guide explains the core techniques behind proxy detection, what signals actually matter, where the limits are, and how you can check any IP address for free.
What Is Proxy Detection?
Proxy Detection: How It Works, Methods & Free Tools - What Is Proxy Detection?.
Proxy detection analyzes an IP address and its surrounding network context to estimate whether the connection is being routed through an intermediary. The goal is not just to label an IP as "proxy" or "not proxy," but to classify the type of anonymization in play.
Common classifications include:
- VPN anonymizers — commercial VPN exit servers
- Open proxies — publicly listed proxies anyone can use
- Web proxies — browser-based proxies that forward HTTP traffic
- Tor exit nodes — the final hop of the Tor network
- Data center ranges — IPs hosted in cloud or server infrastructure
- Residential proxies — IPs assigned to real consumer connections but used as proxies
- Consumer privacy networks — services like Apple Private Relay
- Enterprise private networks — corporate VPNs and dedicated business ranges
A robust proxy detection system combines several of these signals because no single check is reliable on its own.
Why Proxy Detection Matters
Proxy Detection: How It Works, Methods & Free Tools - Why Proxy Detection Matters.
Organizations use proxy detection for very different reasons, but the underlying need is the same: knowing whether a connection is direct or anonymized changes how much trust you should place in it.
Fraud and Abuse Prevention
Fraudsters often route traffic through proxies to hide their real location, create multiple accounts, or bypass geo-blocks. Payment processors and fraud prevention platforms use proxy detection as one input into an IP risk score, which combines proxy signals with reputation data, abuse history, and behavioral patterns to decide whether to approve, challenge, or block a transaction.
Content Licensing and Geo-Restrictions
Streaming services and broadcasters have licensing agreements that limit content to specific countries. When a user connects through a VPN or proxy, the service sees an IP from an allowed region even though the viewer is elsewhere. Proxy detection helps these platforms enforce their regional contracts.
Account Security
A login attempt from a data center IP when the account normally uses a residential connection is a strong signal of credential stuffing or account takeover. Security teams use proxy detection to trigger step-up authentication or block the attempt entirely.
Ad Fraud and Traffic Quality
Advertisers pay for impressions and clicks from real users. Proxy traffic often indicates bots, click farms, or automated scraping, all of which waste budget and skew analytics.
How Proxy Detection Works: Core Techniques
Proxy Detection: How It Works, Methods & Free Tools - How Proxy Detection Works: Core Techniques.
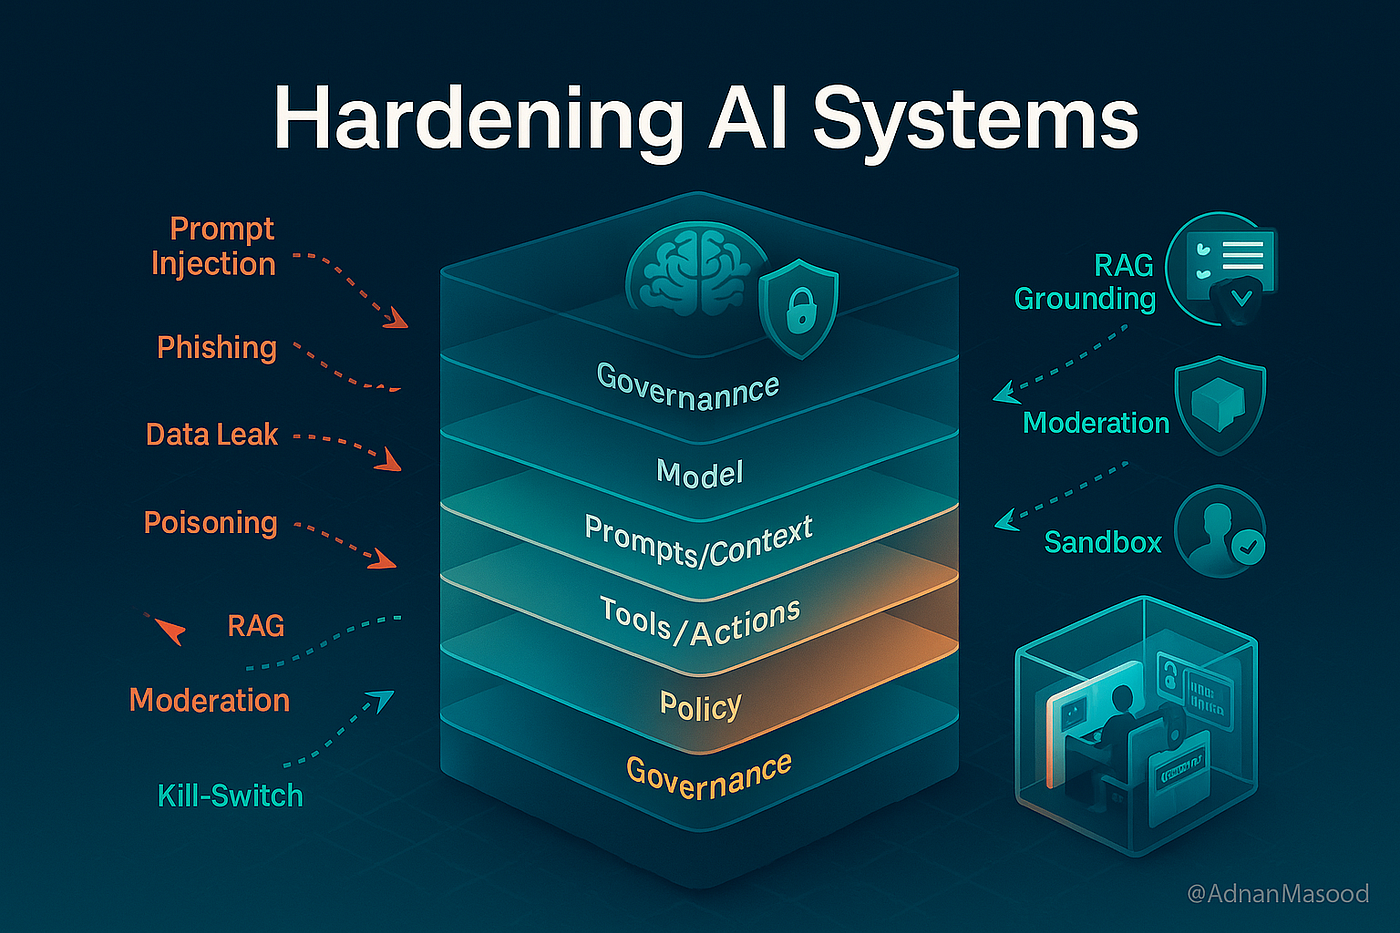
Modern proxy detection is rarely a single lookup. It is a layered analysis that combines network intelligence, IP reputation, infrastructure ownership, and sometimes behavioral signals.
1. Data Center and Hosting Range Matching
Most VPNs and proxies run on servers hosted in data centers. By maintaining databases of IP ranges assigned to cloud providers, hosting companies, and server farms, detection systems can flag any IP that falls within those ranges. This is one of the fastest and most reliable signals, because a residential ISP connection should never appear in a data center range.
2. Public Proxy and VPN Database Matching
Some providers continuously scan the internet for open proxies, public VPN exit servers, and Tor exit nodes, then publish those IPs in regularly updated databases. When an incoming IP matches an entry in one of these databases, it can be flagged immediately. The limitation is coverage: private proxies and newly deployed VPN servers may not appear in public lists yet.
3. IP Reputation and Abuse History
An IP that has previously been associated with spam, fraud, credential stuffing, or scraping carries a poor reputation. Reputation systems aggregate this history and use it as a probabilistic signal. A high-risk IP is more likely to be a proxy or VPN, even if it is not currently listed in a proxy database.
4. ASN and Infrastructure Ownership Analysis
The Autonomous System Number (ASN) reveals which organization controls a block of IPs. Some ASNs are almost exclusively used by hosting providers, while others belong to residential ISPs. Analyzing the ASN, its historical usage patterns, and the ratio of data center to residential IPs within it adds context that a simple range check misses.
5. Behavioral and Fingerprint Signals
Network-level checks can be supplemented with browser-side signals. A browser fingerprint that claims a residential IP in New York but reports a timezone in Moscow, a Russian keyboard layout, and a system language of ru-RU is suspicious. These mismatches do not prove proxy use by themselves, but they strengthen the overall assessment.
Proxy Detection Accuracy: What to Expect
Proxy Detection: How It Works, Methods & Free Tools - Proxy Detection Accuracy: What to Expect.
No proxy detection system is 100% accurate. Public tools often cite accuracy rates around 95%, but that number depends heavily on the test dataset and the types of proxies being detected.
Key limitations to understand:
- Private proxies are hard to detect. A proxy that is not publicly listed and runs on a residential IP may look identical to a normal user connection.
- Residential proxy networks blur the line. These services route traffic through real consumer devices, so the IP is genuinely residential. Detection relies on reputation, traffic patterns, and behavioral signals rather than infrastructure checks.
- False positives happen. Legitimate users on corporate VPNs, privacy-focused ISPs, or mobile carrier NATs can sometimes be flagged as proxies.
- Databases age quickly. VPN providers rotate IPs frequently, so a detection database is only as good as its last update.
For high-stakes decisions, proxy detection should be one signal among many, not a standalone verdict.
How to Check an IP Address for Proxy or VPN Use
If you want to test a specific IP address, several free tools can help.
Online Proxy Detection Lookups
Web-based lookup tools let you enter an IP address and receive a proxy or VPN classification along with supporting data such as country, city, ISP, ASN, and usage type. These are useful for one-off checks and manual investigations. Many commercial providers, including IPQS and IP2Proxy, offer free demo lookups that show the type of data returned by their paid APIs.
API-Based Detection for Developers
For automated checks at scale, a proxy detection API is the practical choice. You send an IP address in a request and receive a JSON response with the proxy classification, threat level, and related metadata. This is the standard approach for integrating proxy detection into signup flows, payment processing, or fraud scoring pipelines.
Browser-Based Privacy Testing
If you want to verify your own connection rather than investigate someone else's IP, a browser-based testing platform is faster and more convenient. BrowserScan provides a free suite of online privacy and security tests that run directly in your browser, including an IP address lookup with geolocation, ISP details, and proxy detection. You can also run DNS and WebRTC leak tests to confirm your VPN is not exposing your real IP, and analyze your browser fingerprint to see how trackers and anti-fraud systems might identify your device. For a more complete picture of what your connection reveals, see this guide on how to use BrowserLeaks for step-by-step privacy testing.
Proxy Detection vs. IP Geolocation
Proxy detection and IP geolocation are related but distinct. Geolocation maps an IP to a physical location, ISP, and ASN. Proxy detection asks whether that IP is being used as an anonymizing intermediary. A proxy detection result often includes geolocation data, but the reverse is not true: knowing an IP is in Frankfurt does not tell you whether it is a VPN exit server in Frankfurt or a residential connection in Frankfurt.
In practice, the two are combined. A fraud system might first geolocate an IP, then check whether the location is consistent with the user's stated address, and finally run proxy detection to see whether the IP is an anonymizer. This layered approach reduces both false positives and false negatives.
Choosing a Proxy Detection Approach
Your choice depends on volume, latency requirements, and how the result will be used.
| Approach | Best For | Trade-offs |
|---|---|---|
| Free online lookup | Manual checks, occasional investigations | Not automated, limited query volume |
| API integration | Real-time decisions at scale | Requires development work, per-query cost |
| Local database | High-volume, low-latency, offline use | Requires hosting and regular updates |
| Browser-based testing | Verifying your own connection and privacy setup | Not designed for checking third-party IPs |
For most production systems, an API is the right balance of speed, accuracy, and ease of integration. For personal privacy checks, a browser-based tool is usually sufficient and requires no installation.
Related reading
- HackerTarget Tutorial: Master OSINT, Scans & Network Tools - A practical HackerTarget tutorial covering Recon-ng for OSINT, hosted Nmap and OpenVAS scanners, and how to verify your setup with privacy testing tools.
- How to Use PrivacyTools.io: A Practical Privacy Guide - Learn how to use PrivacyTools.io to find private software alternatives, understand the recommendations, and verify your setup with privacy testing tools.
Sources and further reading
- Proxy Detection Test | Detect Proxies With Our IP Lookup - IPQS - IPQS analyzes network intelligence, IP reputation, infrastructure ownership, behavioral patterns, and anonymization signals to help detect VPN connections, ...
- IP2Proxy Proxy VPN Detection - Check Proxy & VPN using IP Address - IP2Proxy detects anonymous & open proxy, web proxy, VPN, TOR, Data Center, Search Engine Spider (SES), residential proxy (RES) using IP address in real-time.
- VPN & Proxy Detection Tool - Our VPN and Proxy Detection Tool analyze if an IP Address is either a VPN or proxy. Our goal is to help fight and prevent abuse, attacks, and spam.
Frequently Asked Questions
Can proxy detection identify all VPNs?
No. Detection systems are strong at identifying VPNs that exit through known data center ranges or appear in public databases. VPNs that use residential IPs, rotate exits frequently, or are newly deployed may evade detection for a period.
How accurate is proxy detection?
Public tools often report around 95% accuracy on standard test sets, but real-world accuracy varies by proxy type. Data center VPNs and open proxies are detected reliably. Private residential proxies are much harder to identify and produce more false negatives.
What is the difference between a proxy and a VPN in detection terms?
Technically, a VPN is a type of proxy that encrypts traffic and routes it through a remote server. From a detection standpoint, both are anonymizing intermediaries, and most detection systems classify them together. The practical difference is that VPNs are more likely to use dedicated data center infrastructure, while proxies include a wider range of setups including web proxies and residential proxies.
Can I detect a proxy from a browser fingerprint alone?
Browser fingerprinting can reveal inconsistencies that suggest a proxy or VPN, such as a mismatch between the IP's geolocation and the browser's timezone or language settings. However, fingerprint signals are circumstantial and should be combined with network-level checks for reliable results.
Is proxy detection legal?
Yes. Analyzing IP addresses and network metadata is a standard security and fraud prevention practice. However, how you use the results matters: blocking legitimate users based on proxy use may violate terms of service or regional regulations, so organizations should apply detection results proportionally.
What is the difference between proxy detection and an IP risk score?
Proxy detection answers a specific question: is this IP an anonymizer? An IP risk score is broader, combining proxy signals with abuse history, reputation, velocity, and other factors into a single risk rating. Proxy detection is often one component of a risk score. Learn more in this guide to IP risk scores and how they work.
Conclusion
Proxy detection is a layered discipline, not a single lookup. The most reliable systems combine data center range matching, public proxy databases, IP reputation, ASN analysis, and behavioral signals to classify IPs as VPNs, open proxies, Tor exits, residential proxies, or legitimate connections. Accuracy is high for common anonymizers but drops for private and residential proxy networks, so detection should always be part of a broader risk assessment rather than a standalone gate.
For manual checks, free online lookups and browser-based testing tools cover most needs. For production use, a proxy detection API provides the speed and automation required for real-time decisions. And if your goal is to understand what your own connection reveals, running a browser-based privacy test with IP lookup and proxy detection is a practical first step toward closing the gaps.